What each check looks for, what it can show, and where it falls short.
Digital Signature (C2PA)
Looks for authenticated Content Credentials.
C2PA (Coalition for Content Provenance and Authenticity)
is a standard for embedding provenance records -- called
manifests -- directly into media files. A manifest
documents where a file came from, what tools created or modified it,
and who vouched for it. It's cryptographically signed, so any
post-signing tampering breaks the signature.
Many major AI image generators sign their output with C2PA, including OpenAI's
ChatGPT Images (currently ChatGPT Images 2.5), Google's Nano Banana Pro and Nano
Banana 2, Adobe Firefly, and Anthropic's Claude. So do editing tools like Photoshop and Lightroom,
and capture devices from Leica, Sony, and Canon cameras to Google Pixel phones.
Notable holdouts include Midjourney and FLUX.
Because both AI generators and cameras use C2PA, the manifest's
content matters more than its presence. A manifest claiming
digitalSourceType: trainedAlgorithmicMedia means the
signer says the image is AI-generated;
digitalSourceType: digitalCapture means the signer says a
camera captured it. Trace Machine surfaces these signals for you.
A manifest can also live online instead of inside the file, with the image's
metadata pointing to it. Trace Machine follows that pointer and validates the
manifest the same way. If the pointer leads nowhere, the report says the image
references Content Credentials that couldn't be retrieved.
What C2PA can show
Integrity: the image hasn't been altered since
signing -- even a single changed pixel breaks the signature.
Claimed origin: the signer's assertions about how
the image was made (AI-generated, camera-captured, edited, etc.).
Edit history: a chain of prior manifests
("ingredients") showing transformations over time, if all tools in
the chain supported C2PA.
What C2PA cannot prove
A manifest records claims made by the signer -- it doesn't
independently verify them. "Camera capture" in a manifest proves the
signer said it was a camera capture, not that a camera
actually took the photo. Claims are only as trustworthy as the signer.
Can you forge a C2PA manifest?
Yes. Anyone can create a cryptographically valid manifest using free,
open-source tools. What a forger can't easily do is get their
certificate onto a recognized trust list -- the
registry of vetted signers maintained by the C2PA organization.
Trace Machine checks whether the signing certificate is on a trust
list and tells you the result.
Important limitation: Trust-list recognition isn't
foolproof. The C2PA trust list is maintained by the C2PA organization
itself, not the industry-standard
CCADB infrastructure that
browsers use for HTTPS. Security researchers have demonstrated
forgeries that passed validation on Adobe's Content Credentials site.
C2PA is useful provenance information, not a verdict of authenticity.
Manifests are signed with certificates, and certificates expire.
What happens next depends on whether the signer included an
independent timestamp:
With a TSA timestamp: A Time Stamp Authority
proves the signature was created while the certificate was valid.
The manifest stays verifiable indefinitely.
Without a TSA timestamp: Once the certificate
expires, the manifest can no longer be verified. Many real-world
implementations skip this step.
Trace Machine shows you which kind of timestamp (if any) a manifest
has.
Important limitation: C2PA metadata lives inside the
image file and is easily lost -- screenshots, metadata stripping,
re-encoding, or uploading to most social platforms will erase it.
The absence of a manifest tells you nothing; only its
presence provides information.
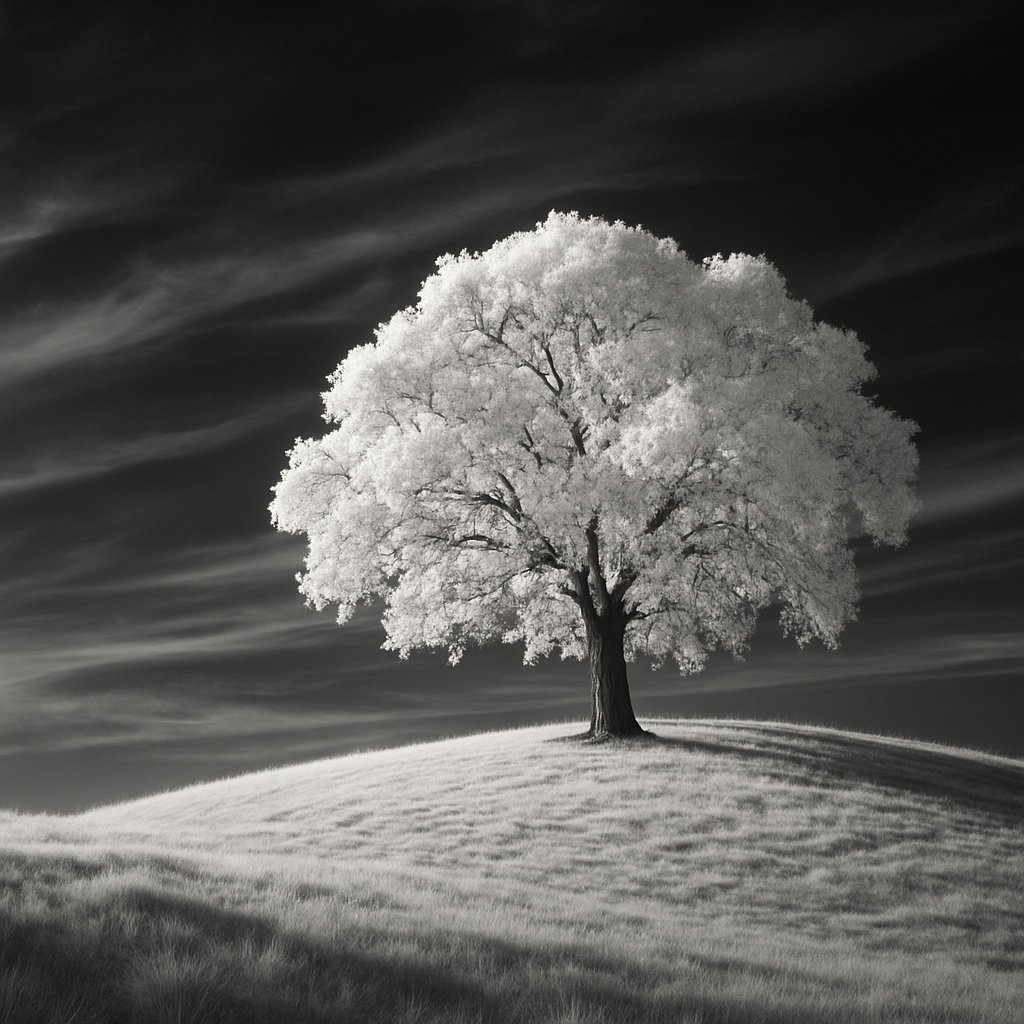
C2PA demo image
Analyze this demo image to see what Trace Machine shows when it
detects a C2PA manifest.
Generated by gpt-image-1 (inside ChatGPT) with the prompt
"An infrared photo of a tree on a hill."
Scans image metadata for hints that common AI tools leave behind.
Image files carry metadata: EXIF camera fields, XMP and IPTC tags, and PNG text
chunks. Some AI tools write their prompt, settings, or an "AI-generated" label
there. Today that's mostly local and open-source tools like ComfyUI, plus
AI-label standards such as IPTC's digital source type and China's TC260.
Mainstream generators now rely on C2PA and invisible watermarks instead.
Important limitation: Metadata is trivial to add, edit, or
strip, so it's a clue, not proof, and missing metadata proves nothing.
Demo image: ComfyUI
ComfyUI saves its whole node graph, including the prompt, into the PNG.
Looks for invisible watermarks we can read locally, like Adobe's TrustMark.
Some watermarks can be read without asking the company that made them. Trace
Machine checks for these on every image, on its own server.
Adobe TrustMark
TrustMark is the open watermark behind Adobe's Durable Content
Credentials. It hides a short identifier in the pixels that survives
screenshots, re-compression, and metadata stripping. The identifier links the
image back to its C2PA manifest in a Content Credentials database, so finding
one means the image was registered for Content Credentials even if the
manifest has since been stripped from the file.
A TrustMark marks provenance, not AI generation: cameras, editors, and AI
tools can all apply one. Because a decoder can occasionally "find" a mark in
an ordinary photo by chance, Trace Machine only reports a mark when it also
reads the same identifier from slightly edited copies of the image.
Important limitation: These checks are positive-only. A hit
is useful evidence, but a miss does not mean the image is clean: most
invisible watermarks (including Google's SynthID and Meta's Content Seal)
can only be read by their makers, and heavy edits can erase any of them.
Collects manual reports from public provider-specific verification portals.
Some AI providers hide an imperceptible watermark in the pixels of every image
they generate. Unlike metadata, these watermarks survive screenshots, resizing,
and re-encoding reasonably well, but only the provider can read them, through
its own public checker. Trace Machine links you to those checkers ("portals")
and records what people report back.
The checks, in order
Automated check (OpenAI): OpenAI licensed SynthID from
Google and embeds it, alongside a C2PA manifest, in images from ChatGPT
Images and its API. Where it's enabled, Trace Machine can check for both
with one click through OpenAI's API. Those results are labeled as automated
checks and count for more than community reports. It only finds OpenAI
images, so if it finds nothing or fails, move on.
Google SynthID Detector: Google embeds SynthID in images
from Gemini and its Nano Banana models, and partners like OpenAI embed it
too. Google's official
SynthID Detector
reads all of them and says which provider made the image, so you report
"Says Google" or "Says OpenAI". You'll need to sign in with a Google,
Apple, or ChatGPT account.
Meta Identify: Meta uses its own imperceptible watermark,
Content Seal, for images from Meta AI. It isn't compatible with SynthID or
C2PA, so it has its own checker.
If you can't use the SynthID Detector (it's rate-limited, or you'd rather
not sign in), OpenAI Verify also checks OpenAI images for both Content
Credentials and SynthID.
Important limitation: Each portal only recognizes the
watermarks it was built for. A negative result rules out those watermarks,
not AI in general, and many generators don't watermark at all. Portal reports on Trace
Machine are community evidence: a negative report means someone checked and
got no positive result.
Compares this upload to prior submissions and shows community votes.
Some our best tools for distinguishing synthetic media are our eyes and minds. Trace Machine maintains a community database of image consensus, where users can vote on whether an image is AI-generated or not.
Important limitation: The unfortunate truth is that synthetic media is a powerful tool for deception -- people may want to misrepresent an AI-generated image as real or vice versa. You're welcome to vote because an image "looks AI-generated" or "looks real," but if you're not sure, err on the side of caution and abstain from voting. Human consensus is not infallible; treat it as what it is: just one data point among many.